News
Moving Offices? Make Sure Your IT Is Ready on Day One
Article Summary: An office move involves more than relocating computers. This guide explains how to involve your IT provider early, arrange internet service ahead of time, back up important data, and test the new space before employees arrive, so your team can work without interruption from the first morning.
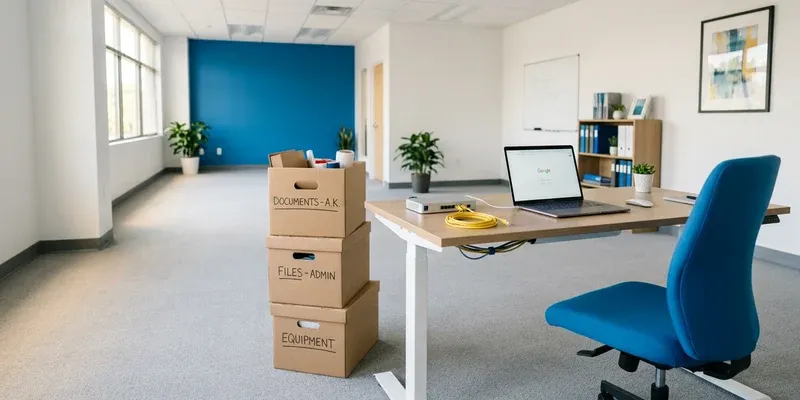
An office move comes with a long list of decisions, including lease dates, furniture, movers, insurance, and staff schedules. On most of those lists, the technology appears as a single line that reads "move the IT," which sounds like a simple job of packing the computers and plugging them back in.
Those computers depend on internet service, cabling, Wi-Fi, phones, printers, and cloud applications, and several of those may not be ready at the new address. If one is missed, employees can arrive on the first morning and find they cannot sign in, make calls, print, process payments, or reach their files. Most of these problems can be avoided when the IT work begins early.
Bring In Your IT Provider Before The Date Is Set
Tell your IT provider about the move as soon as the new location becomes a serious option. If possible, ask them to inspect the premises before you sign the lease, so they can check for suitable internet services, enough network cabling, space for equipment, and the power your setup needs. A modern-looking office does not guarantee usable cabling, and building management may control when providers can enter and which contractors can work in shared areas.
Assign A Coordinator And Build A Timeline
Office moves involve property managers, internet providers, cabling contractors, movers, and your own employees. It helps to choose one person inside the business to track dates and approve changes. Your IT provider should give you a timeline covering internet installation, cabling, equipment setup, testing, staff communication, and the date old services can be canceled. It should also leave time between installing the new systems and moving your team.
Map What Your Business Depends On
Before deciding how to move anything, write down what the business does each day, such as answering calls, taking card payments, accessing customer records, or joining video meetings. Then identify the technology behind each activity. For example, a cloud accounting system needs working internet, user accounts, multi-factor authentication, and access to any connected scanners or printers.
This review often turns up equipment that nobody thought of as IT: door access systems, security cameras, intercoms, alarms, and meeting-room screens. The NIST Cybersecurity Framework 2.0 recommends keeping an inventory of the hardware, software, systems, and services a business relies on. Having that inventory also reduces the chance of leaving something behind during a move.
Arrange Internet, Phones, And The Network Early
Order the internet connection first
Installation can involve surveys, building approval, cabling work, and an engineer visit, so it's best to order as soon as you know what the office needs. Ask the provider to confirm the installation date, the activation date, and any work the landlord or your contractors must finish. If losing internet access would stop the business, discuss a backup connection and test it, since a second service doesn't help if the firewall isn't set up to use it.
Keep the old office connection active until the new one has been installed, tested, and used successfully. Canceling it too early removes a fallback if the move date changes.
Check phones, alarms, and payment terminals
Many business phone systems now run over the internet. Ask your phone provider whether your numbers can be moved, handsets need reconfiguring, and if the emergency calling address needs updating. Alarms, intercoms, entry systems, and payment terminals deserve the same check. Older phone lines are being phased out for digital services, so equipment that relies on an analog line may need an adapter, a replacement, or its own cellular connection.
Review the network for the new space
Moving the old router and switches without a review can carry old problems into the new office. Your IT provider should confirm that the firewall, switches, and wireless access points suit the layout. Then test Wi-Fi from the places where people will actually work, including meeting rooms and reception. If any of your systems restrict access by public IP address, tell those vendors about the move. A new internet service may use a different address and block access to cloud systems, supplier portals, or remote connections.
Protect Your Data And Your Equipment
Confirm that important data is backed up before anything is moved, then check that the latest backups completed and can be restored. NIST recommends creating, protecting, maintaining, and testing backups. Cloud software may protect some information, but it does not automatically cover every device, application, or configuration. Ask your IT provider what would need to be rebuilt if a device were damaged in transit.
Decide early which equipment moves and which gets replaced. Simply moving an old switch or failing printer doesn't guarantee the problem will go away in the new office. Keep a record of every device being transported, including its serial number and intended location. Be sure to label cables, power supplies, and adapters so the right parts arrive together. Small items such as backup drives and security keys are easy to lose among general boxes, so keep them in tracked containers with one person responsible for handing them over.
Test, Cut Over, And Close Out The Old Office
Decide when staff will stop working at the old office and when systems will be available at the new one. Avoid software or account changes that are not required for the move during that period, since unrelated changes make problems harder to trace. Agree in advance which systems come back first. Internet, firewall services, and phones are more urgent than meeting-room screens.
Once the new network is running, test it from the places and devices your staff will use:
Sign in to business applications
Make internal and external calls and join a video meeting
Send a test print job and scan a document
Confirm that payment or booking systems can connect
Check remote access, security cameras, door access, and alarms
Testing from one laptop beside the router will miss problems in particular rooms or devices, so leave time to fix what turns up before the office opens.
After the move, update network diagrams, asset records, and monitoring tools. Tell your phone providers, alarm companies, and payment processors about the new address. Before returning the keys, inspect the old premises for leftover equipment and any labels or paperwork containing passwords. Equipment that will not be reused should be wiped or destroyed in a way suited to the data it holds, since deleting files may not be sufficient. Cancel old internet, phone, and monitoring contracts only once the new office is working, and keep written confirmation. Having IT support available when staff first arrive also helps, since small issues are easier to fix early.
If you're planning a move, involve your IT provider before dates and contractors are finalized. At qnectU, we can help you plan the move. Start now and click here to schedule a quick 26-minute call to make sure your team can work on day one.
Article FAQs
How early should I involve my IT provider in an office move?
As soon as the new office becomes a serious option. Internet availability, building access, cabling, and equipment requirements can all affect the move schedule and budget. The earlier your provider is involved, the more time you have to plan around them.
Should I cancel the old internet connection before moving?
Keep it active until the new connection has been installed and tested. If the move is delayed or the new service has a fault, the old office may still provide a temporary place to work.
FREE GUIDE
Discover The Truth Nobody Is Telling You About IT Security And The New, Critical Threats That WILL Put Your Business At Risk


Answers To Common Questions
Frequently Asked Questions
Do you offer access to senior IT consultants or a vCSO for oversight and guidance?
Yes, we offer access to senior IT consultants and provide vCSO(Virtual Chief Security Officer) as a service for our clients. Our vCSO service provides your organization with expert leadership and strategic direction tailored to your unique cybersecurity and legal compliance needs. We are here to help you navigate the complexities of cybersecurity and ensure that your security posture is robust, compliant, and capable of addressing evolving cyber threats. Book a call today to get expert help with your company’s cybersecurity and compliance.
Do you have a high level of confidence in your security posture? If so, can you explain why?
We have a high level of confidence in the security posture of our company and our clients. Our security stack includes several components to ensure strong and resilient cybersecurity measures. We provide comprehensive risk management, regular audits and assessments, advanced security technologies, employee training and awareness, and incident response planning. Our systems and solutions follow established industry standards and best practices to keep your company safe and your data secure. Since every company has different risks depending on the data, systems, utilization, and more, we can work with your team to develop a robust security plan and implement the proper measures as needed. Reach out today to strengthen your company’s security posture!
Do you have a Disaster Recovery (DR) plan? If so, what’s in place? Is it tested regularly?
We provide robust Disaster Recovery (DR) plans, covering preventative, detective, and corrective measures. Our DR strategies are tailored to each client’s specific needs and are designed to ensure rapid recovery and continuity of operations in the event of any disaster. These plans are regularly reviewed and tested to guarantee they function effectively and meet the highest standards of resilience and reliability. And if a disaster were to occur outside of regular business hours, we have you covered! At qnectU, we have a response time of mere minutes for emergency after-hours calls, ensuring a rapid response to implement your Disaster Recovery plan. Book a call today to protect your company in the event of a disaster.
Do you perform regular risk assessments?
Here at qnectU, we conduct regular risk assessments as a core part of our risk management strategy. Our process is comprehensive, involving identification, categorization, and response planning for potential security risks, including technical vulnerabilities, access controls, and more. These assessments help us understand, control, and mitigate all forms of cyber risk, ensuring that our security measures are effective and up-to-date. But most importantly, we provide continual risk assessments at pre-determined intervals based on your company’s risk level. This ensures that issues are corrected, new risks are identified, and compliance is properly documented. Want to see how our in-depth business risk assessments work? Book a consultation today to get an in-depth risk assessment of your company’s current network security.
Do you follow proven change management principles?
We are committed to following proven change management principles. We understand the importance of structured and systematic processes in implementing changes that affect cybersecurity protocols and IT environments. Our approach is based on industry-recognized frameworks and methodologies that ensure changes are managed effectively, focusing on minimizing risks, enhancing security posture, and achieving strategic objectives.
Do you address all my compliance needs, including HIPAA?
We specialize in Compliance as a Service (CaaS), and our program is designed to meet a wide range of regulatory requirements to ensure that your business adheres to the highest standards of compliance. We demonstrate our compliance through detailed assessments, documentation, and third-party audits. Our expertise and ongoing support can give you confidence that your company’s sensitive information is managed securely and in full compliance with all regulations.
Is third-party auditing provided to ensure cybersecurity and compliance requirements are being met?
In today’s world a business can easily be compromised via a “supply chain hack.” There have been several instances where the IT company has exposed all of their clients to hacking due to their own lack of cybersecurity measures. In order to prevent this within our own company, we work closely with a third party for comprehensive auditing services to ensure that all cybersecurity and compliance requirements are met. Our rigorous audit process involves a thorough examination of our systems and practices against established industry standards and best practices. This collaboration provides an objective perspective and deep expertise to identify any potential vulnerabilities, ensuring that our cybersecurity measures are robust, up-to-date, and in full compliance with regulatory demands.
What is Compliance as a Service (Caas)?
Compliance as a Service (Caas) means that our experts will give you specialized help in handling all the rules and regulations your business needs to follow. We do this by providing expert guidance to help you determine what rules apply to your business and how to follow them. All while giving ongoing support to monitor your compliance status and updates in regulations. This may also include any advanced tools to help manage compliance tasks and risk management surrounding compliance. CaaS takes the hassle out of compliance so you can focus on running your business with confidence.
Who is Greg Mauer?
Gregory Mauer is the founder and CEO of our company, a best-selling author, speaker, and a cybersecurity & compliance expert. He has been on stage with the likes of the “Nice Shark”, Robert Herjavec, Siri co-founder Adam Cheyer, and business coach and author Mike Michalowicz.
Answers To Common Questions
Frequently Asked Questions
Do you offer access to senior IT consultants or a vCSO for oversight and guidance?
Yes, we offer access to senior IT consultants and provide vCSO(Virtual Chief Security Officer) as a service for our clients. Our vCSO service provides your organization with expert leadership and strategic direction tailored to your unique cybersecurity and legal compliance needs. We are here to help you navigate the complexities of cybersecurity and ensure that your security posture is robust, compliant, and capable of addressing evolving cyber threats. Book a call today to get expert help with your company’s cybersecurity and compliance.
Do you have a high level of confidence in your security posture? If so, can you explain why?
We have a high level of confidence in the security posture of our company and our clients. Our security stack includes several components to ensure strong and resilient cybersecurity measures. We provide comprehensive risk management, regular audits and assessments, advanced security technologies, employee training and awareness, and incident response planning. Our systems and solutions follow established industry standards and best practices to keep your company safe and your data secure. Since every company has different risks depending on the data, systems, utilization, and more, we can work with your team to develop a robust security plan and implement the proper measures as needed. Reach out today to strengthen your company’s security posture!
Do you have a Disaster Recovery (DR) plan? If so, what’s in place? Is it tested regularly?
We provide robust Disaster Recovery (DR) plans, covering preventative, detective, and corrective measures. Our DR strategies are tailored to each client’s specific needs and are designed to ensure rapid recovery and continuity of operations in the event of any disaster. These plans are regularly reviewed and tested to guarantee they function effectively and meet the highest standards of resilience and reliability. And if a disaster were to occur outside of regular business hours, we have you covered! At qnectU, we have a response time of mere minutes for emergency after-hours calls, ensuring a rapid response to implement your Disaster Recovery plan. Book a call today to protect your company in the event of a disaster.
Do you perform regular risk assessments?
Here at qnectU, we conduct regular risk assessments as a core part of our risk management strategy. Our process is comprehensive, involving identification, categorization, and response planning for potential security risks, including technical vulnerabilities, access controls, and more. These assessments help us understand, control, and mitigate all forms of cyber risk, ensuring that our security measures are effective and up-to-date. But most importantly, we provide continual risk assessments at pre-determined intervals based on your company’s risk level. This ensures that issues are corrected, new risks are identified, and compliance is properly documented. Want to see how our in-depth business risk assessments work? Book a consultation today to get an in-depth risk assessment of your company’s current network security.
Do you follow proven change management principles?
We are committed to following proven change management principles. We understand the importance of structured and systematic processes in implementing changes that affect cybersecurity protocols and IT environments. Our approach is based on industry-recognized frameworks and methodologies that ensure changes are managed effectively, focusing on minimizing risks, enhancing security posture, and achieving strategic objectives.
Do you address all my compliance needs, including HIPAA?
We specialize in Compliance as a Service (CaaS), and our program is designed to meet a wide range of regulatory requirements to ensure that your business adheres to the highest standards of compliance. We demonstrate our compliance through detailed assessments, documentation, and third-party audits. Our expertise and ongoing support can give you confidence that your company’s sensitive information is managed securely and in full compliance with all regulations.
Is third-party auditing provided to ensure cybersecurity and compliance requirements are being met?
In today’s world a business can easily be compromised via a “supply chain hack.” There have been several instances where the IT company has exposed all of their clients to hacking due to their own lack of cybersecurity measures. In order to prevent this within our own company, we work closely with a third party for comprehensive auditing services to ensure that all cybersecurity and compliance requirements are met. Our rigorous audit process involves a thorough examination of our systems and practices against established industry standards and best practices. This collaboration provides an objective perspective and deep expertise to identify any potential vulnerabilities, ensuring that our cybersecurity measures are robust, up-to-date, and in full compliance with regulatory demands.
What is Compliance as a Service (Caas)?
Compliance as a Service (Caas) means that our experts will give you specialized help in handling all the rules and regulations your business needs to follow. We do this by providing expert guidance to help you determine what rules apply to your business and how to follow them. All while giving ongoing support to monitor your compliance status and updates in regulations. This may also include any advanced tools to help manage compliance tasks and risk management surrounding compliance. CaaS takes the hassle out of compliance so you can focus on running your business with confidence.
Who is Greg Mauer?
Gregory Mauer is the founder and CEO of our company, a best-selling author, speaker, and a cybersecurity & compliance expert. He has been on stage with the likes of the “Nice Shark”, Robert Herjavec, Siri co-founder Adam Cheyer, and business coach and author Mike Michalowicz.
Innovation
Fresh, creative solutions.
Integrity
Honesty and transparency.
Excellence
Top-notch services.
FOLLOW US


Subscribe to our newsletter!
COMPANY
LEGAL
© Copyright 2026 qnectU